# Python Obfuscator — Obfuscate, Virtualize & Protect Python Code
**[Python Obfuscator](https://www.pelock.com/products/python-obfuscator)** is a tool to obfuscate, virtualize & protect Python `.py` scripts against reverse engineering with a VM engine (or finite-state automata machine), self-defending integrity checks, polymorphic string encryption, anti-debugging, anti-vm, anti-emulation and 50+ total obfuscation strategies!
It's available for Windows & Linux, plus VSCode/Cursor extension:
* https://www.pelock.com/products/python-obfuscator/download
Multiple programming APIs available:
* https://www.pelock.com/products/python-obfuscator/api
An online obfuscator interface:
* https://www.pelock.com/python-obfuscator/
## Why Python scripts need obfuscation?
Scripts are typically distributed as plain `.py` files or bundled inside packages. That convenience means anyone with file access can read the full logic, hunt for credentials or API keys in strings, and steal your algorithms unless you take extra steps to hide intent.
[Python](https://www.python.org/) is one of the most popular general-purpose scripting languages. It is widely used for automation, backend services, data processing, tooling, and licensing/agent code that customers run on their own machines.
## Obfuscation strategies
Python Obfuscator comes with many advanced obfuscation, virtualization & protection strategies. You can easily tune protection versus size and performance.
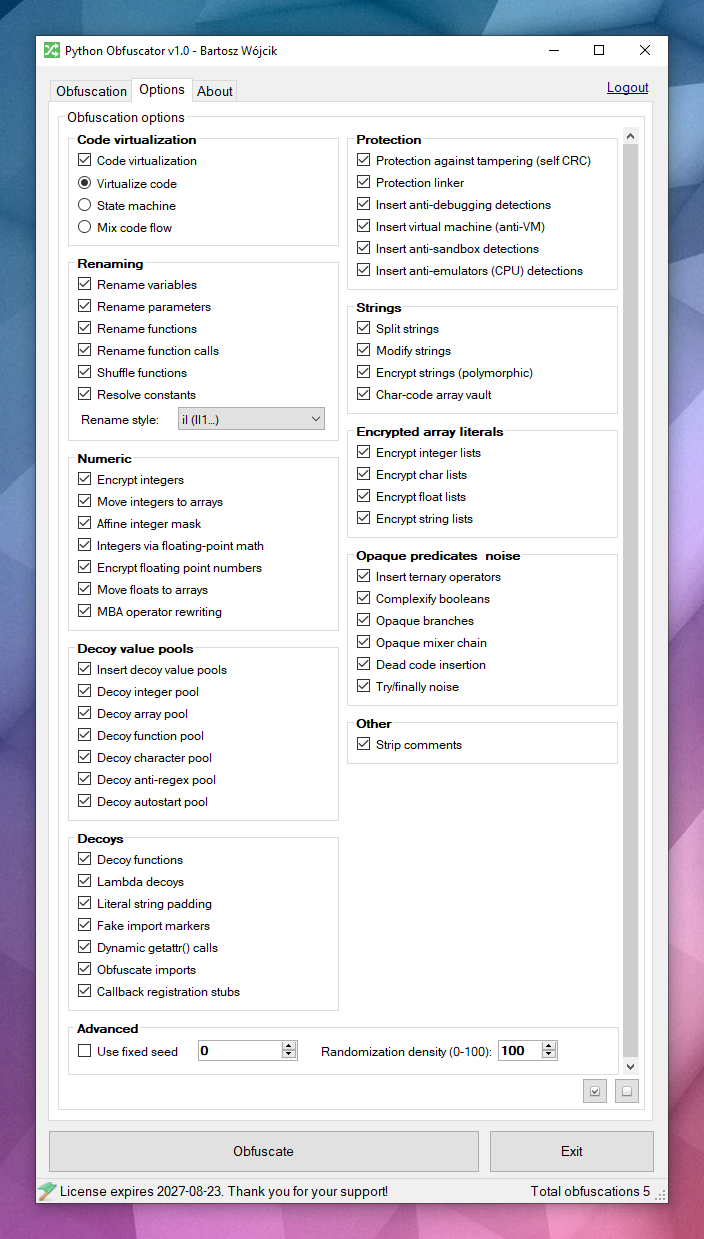
###  Powerful obfuscation
Polymorphic string encryption is the core of the string pipeline: each build generates a fresh decryptor so literals never share one static algorithm. Integers, floats, and decoy noise join that layer. The result conceals literals and structure while preserving tested runtime behaviour.
###  Code virtualization
 is the main control-flow defense. Selected statements are lifted into a randomly generated VM engine (or FSA / flattened dispatcher) with shuffled dispatch tables, decoy opcodes, and an obfuscated dispatcher loop. Analysts must interpret the virtual machine instead of reading plain Python.
###  Finite-state automata (FSA)
 obfuscation rewrites linear Python statement blocks into dual-state automata with opaque schedulers and shuffled dispatch handlers. Instead of reading code top to bottom, analysts must follow numeric states, transition tables, and decoy paths to reconstruct the original order.
###  Anti-debugging
 protection inserts polymorphic probes that detect attached debuggers, tracing hooks, and related host signals, together with anti-VM, anti-sandbox and anti-emulator checks. When a check fires, the obfuscated script exits silently instead of revealing protected logic under interactive analysis.
###  Self-integrity checks
Self-defending integrity checks verify that the obfuscated file has not been patched. A bootstrap probe hashes the on-disk script and sets a tamper key when it no longer matches the obfuscated build. String decryptors consume that key, so edited scripts return garbage instead of plaintext.
###  Protection linker
The protection linker adds decoy functions and fake calls so a copied fragment still looks like real program code. Hidden traps fire only if someone edits the file or runs a piece of it on its own. When the script starts normally, those extras stay silent and the program runs as usual.
## Before and after obfuscation
Look at this example — the same script becomes harder to read at a glance after obfuscation.
### Sample Python script before obfuscation
```python
label = 'SecretKey'
port = 443
def get_sum(a, b):
return a + b
print(label, port)
r = get_sum(11, 31)
print(r)
```
### After obfuscation
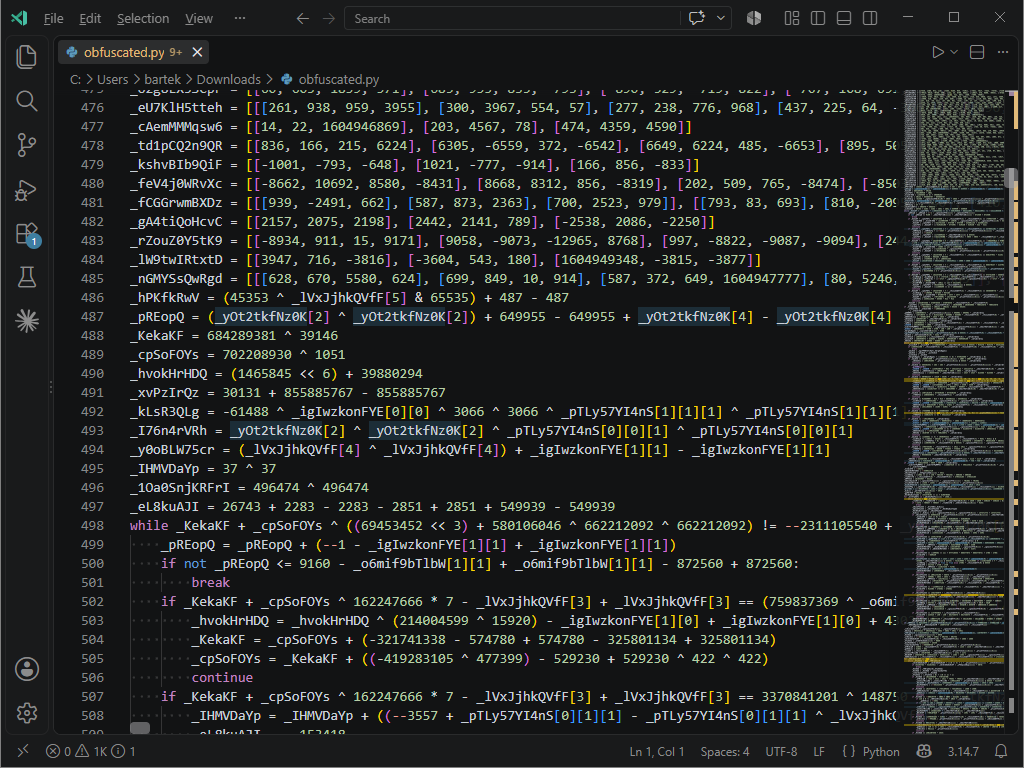
Would you still recognise the original intent if you only had the obfuscated text and no prior copy of the script?
### How does Python Obfuscator work?
The engine parses Python source into an AST tree, then applies selectable transforms. Code virtualization (VM, FSA, or flattening) rewrites execution so analysts cannot read the script top to bottom. Polymorphic string encryption hides literals; self-defending integrity probes detect patched files. Also available: identifier renaming, numeric encryption, noise and decoy insertion, the protection linker, and anti-debugging checks. Many techniques are specific to this product; some ideas are shared with our other protection tools.
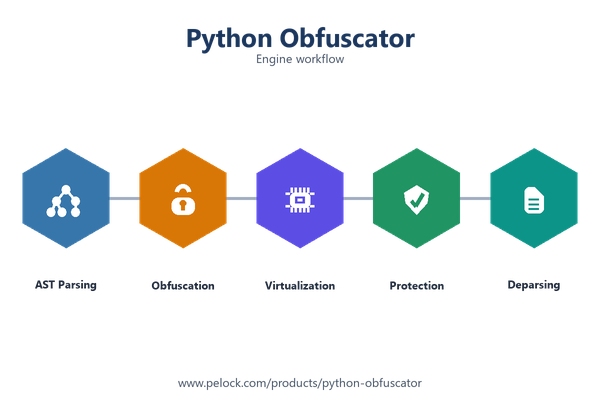
When all passes finish, the engine emits a new `.py` file. Edge cases in the Python grammar and hosting environments mean you should always test the output in your target runtime.
## Protect your Python scripts & algorithms
Take no chances, use **Python Obfuscator** to obfuscate, virtualize and protect your Python scripts and algorithms.
Our company has a long history in obfuscation technologies and code obfuscators (see our [PowerShell](https://www.pelock.com/products/powershell-pro-obfuscator), [Java](https://www.pelock.com/products/jobfuscator), [AutoIt](https://www.pelock.com/products/autoit-obfuscator), [x86 Assembly](https://www.pelock.com/products/obfuscator) & obfuscators).
We actively bugfix, research and develop new obfuscation strategies for our tools.
You can count on our expertise and support in this field.
### Installation
The preferred way of WebApi interface installation is via [crates.io](https://crates.io/).
Run:
```bash
cargo add python-obfuscator
```
Or add this entry directly to your `Cargo.toml` in `[dependencies]`:
```toml
python-obfuscator = "1.0.0"
```
The crate is available at https://crates.io/crates/python-obfuscator
From a checkout of this repository you can run the included examples, for example:
```bash
cargo run --example python-obfuscator-example-simple
```
### Example of obfuscating Python script source code using default options
```rust
/******************************************************************************
* Python Obfuscator WebApi interface usage example.
*
* In this example we will obfuscate sample source with default options.
*
* Version : v1.0.0
* Language : Rust
* Author : Bartosz Wójcik
* Web page : https://www.pelock.com
*
*****************************************************************************/
use python_obfuscator::{PythonObfuscator, PythonObfuscatorResponse};
#[tokio::main]
async fn main() -> Result<(), Box<dyn std::error::Error>> {
//
// include Python Obfuscator class
//
//
// when developing from a repository clone without installing the package use:
//
// use python_obfuscator::{PythonObfuscator, PythonObfuscatorResponse};
// (path dependency in Cargo.toml pointing to this crate)
//
// create Python Obfuscator class instance (we are using our activation key)
//
let my_python_obfuscator =
PythonObfuscator::new(Some("ABCD-ABCD-ABCD-ABCD".to_string()));
//
// source code in Python format
//
let script_source_code = r#"label = 'SecretKey'
port = 443
def get_sum(a, b):
return a + b
print(label, port)
r = get_sum(11, 31)
print(r)"#;
//
// by default all obfuscation options are enabled, so we can just simply call:
//
let result = my_python_obfuscator
.obfuscate_script_source(script_source_code, true)
.await;
//
// it's also possible to pass a Python script file path instead of a string e.g.
//
// let result = my_python_obfuscator
// .obfuscate_script_file(std::path::Path::new("/path/to/project/script.py"), true)
// .await;
//
// result object holds the obfuscation results as well as other information
//
// result.error - error code
// result.output - obfuscated code
// result.demo - demo mode (empty/invalid key); strategy flags ignored; always integers_to_arrays, mba_binops, encrypt_strings (no virt; 1000 char limit)
// result.license_expiration - license end date (Y-m-d), empty if none
// result.usages_total - total obfuscations for this activation code
//
match result {
Some(PythonObfuscatorResponse::Object(obj)) => {
//
// display obfuscated code
//
if obj.error == PythonObfuscator::ERROR_SUCCESS {
println!("{}", obj.output.unwrap_or_default());
} else {
return Err(
format!("An error occurred, error code: {}", obj.error).into(),
);
}
}
Some(PythonObfuscatorResponse::Json(_)) => {}
None => {
return Err("Something unexpected happen while trying to obfuscate the code.".into());
}
}
Ok(())
}
```
### An example of obfuscating Python script source code with customized obfuscation strategies
```rust
/******************************************************************************
* Python Obfuscator WebApi interface usage example.
*
* In this example we will obfuscate sample source with every public option
* set, so you can see the full client surface and turn flags on or off.
*
* Version : v1.0.0
* Language : Rust
* Author : Bartosz Wójcik
* Web page : https://www.pelock.com
*
*****************************************************************************/
use python_obfuscator::{
CodeVirtualization, PythonObfuscator, PythonObfuscatorResponse, RenameStyle,
};
#[tokio::main]
async fn main() -> Result<(), Box<dyn std::error::Error>> {
//
// include Python Obfuscator class
//
//
// when developing from a repository clone without installing the package use:
//
// use python_obfuscator::{PythonObfuscator, PythonObfuscatorResponse};
// (path dependency in Cargo.toml pointing to this crate)
//
// create Python Obfuscator class instance (we are using our activation key)
//
let mut my_python_obfuscator =
PythonObfuscator::new(Some("ABCD-ABCD-ABCD-ABCD".to_string()));
//
// should the source code be compressed (both input & compressed)
//
my_python_obfuscator.enable_compression = false;
//
// globals
//
// fixed random seed for reproducible obfuscation output (optional)
//
my_python_obfuscator.seed = None;
//
// randomization density / intensity (0-100)
//
my_python_obfuscator.randomization_density = None;
//
// identifier renaming style: RenameStyle::Il, O0, Confusable, Hex, Homoglyph, or Mangled
//
my_python_obfuscator.rename_style = Some(RenameStyle::Il);
//
// code virtualization (exactly one): Vm, Fsa, or Flat
// set to None to skip virtualization
//
my_python_obfuscator.code_virtualization = Some(CodeVirtualization::Vm);
//
// protection (opt-in on the service for --all; shown enabled here so every flag is visible)
//
// protection against tampering with protected code (integrity verification)
//
my_python_obfuscator.self_defending = true;
//
// protection linker (decoy call graph; requires self_defending)
//
my_python_obfuscator.protection_linker = true;
//
// insert anti-debugging detections
//
my_python_obfuscator.detect_debugger = true;
//
// insert virtual machine (anti-VM) detections
//
my_python_obfuscator.anti_vm = true;
//
// insert anti-sandbox detections
//
my_python_obfuscator.anti_sandbox = true;
//
// insert anti-emulators (CPU) detections
//
my_python_obfuscator.anti_emulator = true;
//
// renaming
//
// rename variable names to random string values
//
my_python_obfuscator.rename_variables = true;
//
// rename parameter names to random string values
//
my_python_obfuscator.rename_parameters = true;
//
// rename function names to random string values
//
my_python_obfuscator.rename_functions = true;
//
// rename function call references consistently with renamed functions
//
my_python_obfuscator.rename_function_calls = true;
//
// shuffle function order in the output source
//
my_python_obfuscator.shuffle_functions = true;
//
// fold/resolve constant expressions at obfuscation time
//
my_python_obfuscator.resolve_constants = true;
//
// strings
//
// split strings into concatenated chunks
//
my_python_obfuscator.split_strings = true;
//
// apply light transformations/mutations to string literals
//
my_python_obfuscator.modify_strings = true;
//
// encrypt strings using randomly generated polymorphic encryption algorithms
//
my_python_obfuscator.encrypt_strings = true;
//
// store string fragments in char-code array vaults
//
my_python_obfuscator.string_char_array_vault = true;
//
// numeric
//
// encrypt integers
//
my_python_obfuscator.encrypt_integers = true;
//
// encrypt floating point numbers
//
my_python_obfuscator.encrypt_floating = true;
//
// replace binary operators with mixed boolean-arithmetic (MBA) equivalents
//
my_python_obfuscator.mba_binops = true;
//
// represent integers via floating-point math
//
my_python_obfuscator.integers_to_floating = true;
//
// move integers to arrays
//
my_python_obfuscator.integers_to_arrays = true;
//
// move floats to arrays
//
my_python_obfuscator.floats_to_arrays = true;
//
// apply redundant xor / affine integer masks
//
my_python_obfuscator.affine_integer_mask = true;
//
// encrypted array literals
//
// encrypt integer array literals
//
my_python_obfuscator.array_int_crypt = true;
//
// encrypt character array literals
//
my_python_obfuscator.array_char_crypt = true;
//
// encrypt floating-point array literals
//
my_python_obfuscator.array_double_crypt = true;
//
// encrypt string array literals
//
my_python_obfuscator.array_string_crypt = true;
//
// decoy value pools
//
// insert a shared bucket of random noise values used by other strategies
//
my_python_obfuscator.insert_random_value_bucket = true;
//
// populate the random value bucket with decoy integers
//
my_python_obfuscator.random_bucket_integers = true;
//
// populate the random value bucket with decoy arrays
//
my_python_obfuscator.random_bucket_arrays = true;
//
// populate the random value bucket with decoy functions
//
my_python_obfuscator.random_bucket_functions = true;
//
// populate the random value bucket with decoy characters
//
my_python_obfuscator.random_bucket_characters = true;
//
// populate the random value bucket with anti-regex decoy noise
//
my_python_obfuscator.random_bucket_anti_regex = true;
//
// populate the random value bucket with autostart decoy stubs
//
my_python_obfuscator.random_bucket_autostart = true;
//
// opaque predicates & noise
//
// rewrite selected statements using ternary operators
//
my_python_obfuscator.insert_ternary_operators = true;
//
// replace boolean conditions with equivalent complex expressions
//
my_python_obfuscator.complexify_booleans = true;
//
// insert opaque predicate branches
//
my_python_obfuscator.opaque_branches = true;
//
// insert opaque mixer chains into control flow
//
my_python_obfuscator.opaque_mixer_chain = true;
//
// insert dead code
//
my_python_obfuscator.insert_dead_code = true;
//
// wrap code in try/finally blocks with dead noise
//
my_python_obfuscator.try_finally_noise = true;
//
// decoys
//
// insert decoy functions
//
my_python_obfuscator.decoy_functions = true;
//
// insert decoy lambda expressions
//
my_python_obfuscator.lambda_decoys = true;
//
// insert literal padding noise
//
my_python_obfuscator.literal_padding = true;
//
// insert fake import statement markers
//
my_python_obfuscator.fake_import_markers = true;
//
// use dynamic getattr()-based indirect calls
//
my_python_obfuscator.dynamic_getattr_calls = true;
//
// rewrite absolute imports into __import__ / getattr
//
my_python_obfuscator.obfuscate_imports = true;
//
// insert dead callback/event registration stubs
//
my_python_obfuscator.callback_registration_stubs = true;
//
// other
//
// strip comments from the output source
//
my_python_obfuscator.remove_comments = true;
//
// source code in Python format
//
let script_source_code = r#"label = 'SecretKey'
port = 443
def get_sum(a, b):
return a + b
print(label, port)
r = get_sum(11, 31)
print(r)"#;
//
// obfuscate the source code with the options set above
//
let result = my_python_obfuscator
.obfuscate_script_source(script_source_code, true)
.await;
//
// it's also possible to pass a Python script file path instead of a string e.g.
//
// let result = my_python_obfuscator
// .obfuscate_script_file(std::path::Path::new("/path/to/project/script.py"), true)
// .await;
//
// result object holds the obfuscation results as well as other information
//
// result.error - error code
// result.output - obfuscated code
// result.demo - demo mode (empty/invalid key); strategy flags ignored; always integers_to_arrays, mba_binops, encrypt_strings (no virt; 1000 char limit)
// result.license_expiration - license end date (Y-m-d), empty if none
// result.usages_total - total obfuscations for this activation code
//
match result {
Some(PythonObfuscatorResponse::Object(obj)) => {
//
// display obfuscated code
//
if obj.error == PythonObfuscator::ERROR_SUCCESS {
println!("{}", obj.output.unwrap_or_default());
} else {
return Err(
format!("An error occurred, error code: {}", obj.error).into(),
);
}
}
Some(PythonObfuscatorResponse::Json(_)) => {}
None => {
return Err("Something unexpected happen while trying to obfuscate the code.".into());
}
}
Ok(())
}
```
### Check activation key status
```rust
/******************************************************************************
* Python Obfuscator WebApi interface usage example.
*
* In this example we will verify our activation key status.
*
* Version : v1.0.0
* Language : Rust
* Author : Bartosz Wójcik
* Web page : https://www.pelock.com
*
*****************************************************************************/
use python_obfuscator::{PythonObfuscator, PythonObfuscatorResponse};
#[tokio::main]
async fn main() -> Result<(), Box<dyn std::error::Error>> {
//
// include Python Obfuscator class
//
//
// if you don't want to use crates.io use a path dependency to this crate
//
// [dependencies]
// python-obfuscator = { path = ".." }
//
// create Python Obfuscator class instance (we are using our activation key)
//
let my_python_obfuscator =
PythonObfuscator::new(Some("ABCD-ABCD-ABCD-ABCD".to_string()));
//
// login to the service
//
let result = my_python_obfuscator.login(true).await;
//
// result object holds the information about the license
//
// result.demo - demo mode (empty/invalid key); strategy flags ignored; always integers_to_arrays, mba_binops, encrypt_strings (no virt; 1000 char limit)
// result.license_expiration - license end date (Y-m-d), empty if none
// result.usages_total - total obfuscations for this activation code
// result.string_limit - max. source code size allowed (it's 1000 bytes for demo mode)
//
match result {
Some(PythonObfuscatorResponse::Object(obj)) => {
println!(
"Demo version status - {}",
if obj.demo.unwrap_or(false) {
"true"
} else {
"false"
}
);
println!(
"License expiration - {:?}",
obj.license_expiration
);
println!(
"Total obfuscations - {}",
obj.usages_total.unwrap_or(0)
);
println!(
"Max. source code size - {}",
obj.string_limit.unwrap_or(0)
);
}
Some(PythonObfuscatorResponse::Json(_)) => {}
None => {
return Err("Something unexpected happen while trying to login to the service.".into());
}
}
Ok(())
}
```
## Skip selected functions and classes
Use the [Python Obfuscator Decorator](https://github.com/PELock/Python-Obfuscator-Decorator) package to mark functions and classes that should skip chosen strategies. You need it only to **run original source**. The obfuscator reads `@obfuscator.skip` from the AST, applies the skip, then **strips** the decorator and unused `import obfuscator` lines. Obfuscated output has no runtime dependency on this package.
Package on PyPI: https://pypi.org/project/python-obfuscator-decorator/
### Installation
```
pip install python-obfuscator-decorator
```
or
```
python3 -m pip install python-obfuscator-decorator
```
Import package name: **`obfuscator`**. PyPI distribution name: **`python-obfuscator-decorator`**.
### Simple usage
```python
import obfuscator
@obfuscator.skip()
def handshake(secret: str) -> str:
"""Skip every mutating strategy on this function."""
return secret
```
Also valid:
- `@obfuscator.skip(obfuscator.ENCRYPT_STRINGS, obfuscator.CODE_VIRTUALIZATION)` — skip listed strategies
- `@obfuscator.skip("encrypt_strings")` — string keys match engine strategy names
- `@obfuscator.skip` (bare, no call) — skip every mutating strategy on that construct
- `import obfuscator as alias` then `@alias.skip(...)`
`CODE_VIRTUALIZATION` skips all virtualization modes (VM, FSA, flatten) on that function or class.
## Use Python Obfuscator Online
Online interface for Python Obfuscator is available at:
https://www.pelock.com/python-obfuscator/
## Windows GUI client and command line version
You can download it at:
https://www.pelock.com/products/python-obfuscator/download
#### Python Obfuscator comes also with full GUI version for Windows
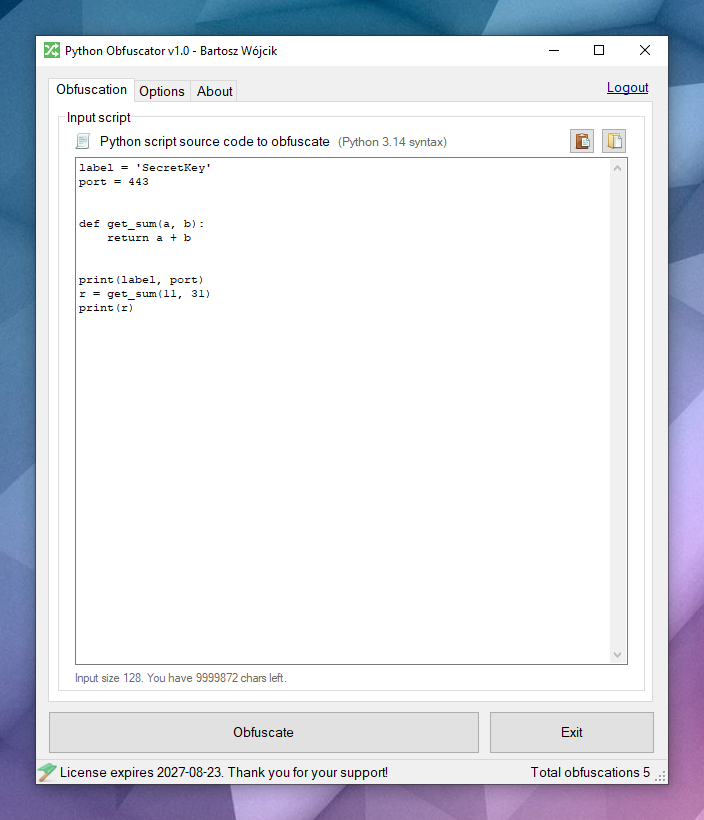
#### Obfuscation options

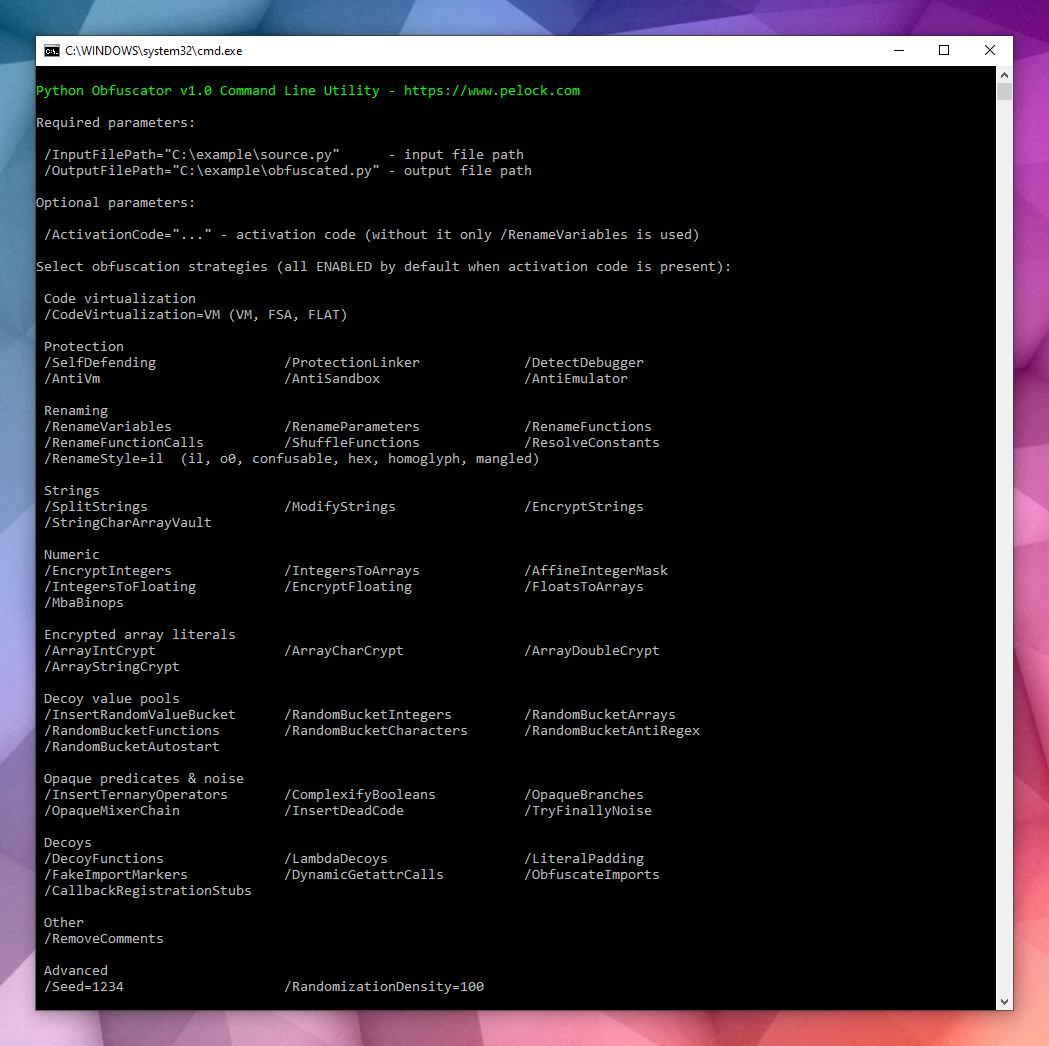
#### Command line interface aka CLI
Python Obfuscator ships with a command-line interface for Windows and Linux automation. Use it to integrate obfuscation into build servers, CI jobs, or batch packaging.
## Demo mode limitations
In demo mode the obfuscator always applies `integers_to_arrays`, `mba_binops`, and `encrypt_strings` (no code virtualization). Source size is limited to 1000 characters.
Bartosz Wójcik
* Visit my site at — https://www.pelock.com
* X — https://x.com/PELock
* GitHub — https://github.com/PELock